Black October Hit Crypto. Then It Hit Your IDE.
Binance lost $6.3B. A backdoored Claude Code extension planted SSH keys. Azure leaked across tenants. October 2026 changed everything.
ComputeLeap Team
Black October Hit Crypto. Then It Hit Your IDE.
The largest theft in human history happened on October 29, 2026. North Korea's TraderTraitor group drained $6.36 billion from Binance in roughly 20 minutes — across ten blockchains, through compromised hot wallet signing infrastructure. But that is not the real story of October 2026.
The real story is what happened next. Within 24 hours of the Binance hack, the front page of Hacker News was dominated not by one breach, but by five: a backdoored Claude Code extension planting SSH keys on developer machines, five cross-tenant Azure compromises, a Linode security incident, a Bunny CDN breach via Gcore, and AO3 taken offline for investigation. Five of HN's top twelve stories on a single day were security incidents. One commenter captured the mood: "I guess this is just going to be the next few months/years, as HN right now is just breach after breach."
This is not a coincidence. This is the month the attack surface expanded from stealing money to compromising the tools that build everything.
The $6.3 Billion Heist: What Actually Happened
TRM Labs' forensic analysis paints a picture of surgical precision. The attacker — attributed to North Korea's TraderTraitor with "high confidence" — compromised Binance's hot wallet signing infrastructure. On Ethereum, they used an EIP-7702 delegation: the Binance hot wallet signed 50 authorizations pointing to a sweeper contract that only the attacker could control.
The timeline is staggering:
- 20:05 UTC — Five Binance XRP wallets send 233.46 million XRP
- 20:20 — The Bitcoin hot wallet sends 18,270 BTC ($1.47 billion); the Ethereum delegation transaction is submitted
- 20:23 — The entire Ethereum hot wallet balance is swept, including 1.615 billion USDT
- 20:41 to 23:56 — Secondary sweeps hit remaining chains
- 21:01 — Tether freezes $971 million USDT (11 minutes after the first ETH sweep)
- 23:35 — Binance reports $2.54 billion frozen
The total haul: approximately $6.36 billion across ten blockchains. About $2.7 billion was frozen by stablecoin issuers and chain-level interventions (Tether, Circle, Ripple, Arbitrum Security Council). The attacker still holds approximately $2.4 billion in assets beyond any issuer's reach.
For context: the February 2025 Bybit hack — previously the largest crypto theft — was $1.5 billion. The Binance hack is more than four times larger. TRM notes shared patterns between the two: small Tornado Cash withdrawals funding an operator wallet, pre-staging, and pre-obtained signatures executed in a single burst.
The Community's Verdict
The internet reacted instantly. On Reddit, two threads in r/technology accumulated over 45,000 combined upvotes — one on the TRM Labs report (31,509 upvotes, 1,970 comments) and another on Wired's "20 minutes" angle (13,723 upvotes, 1,543 comments).
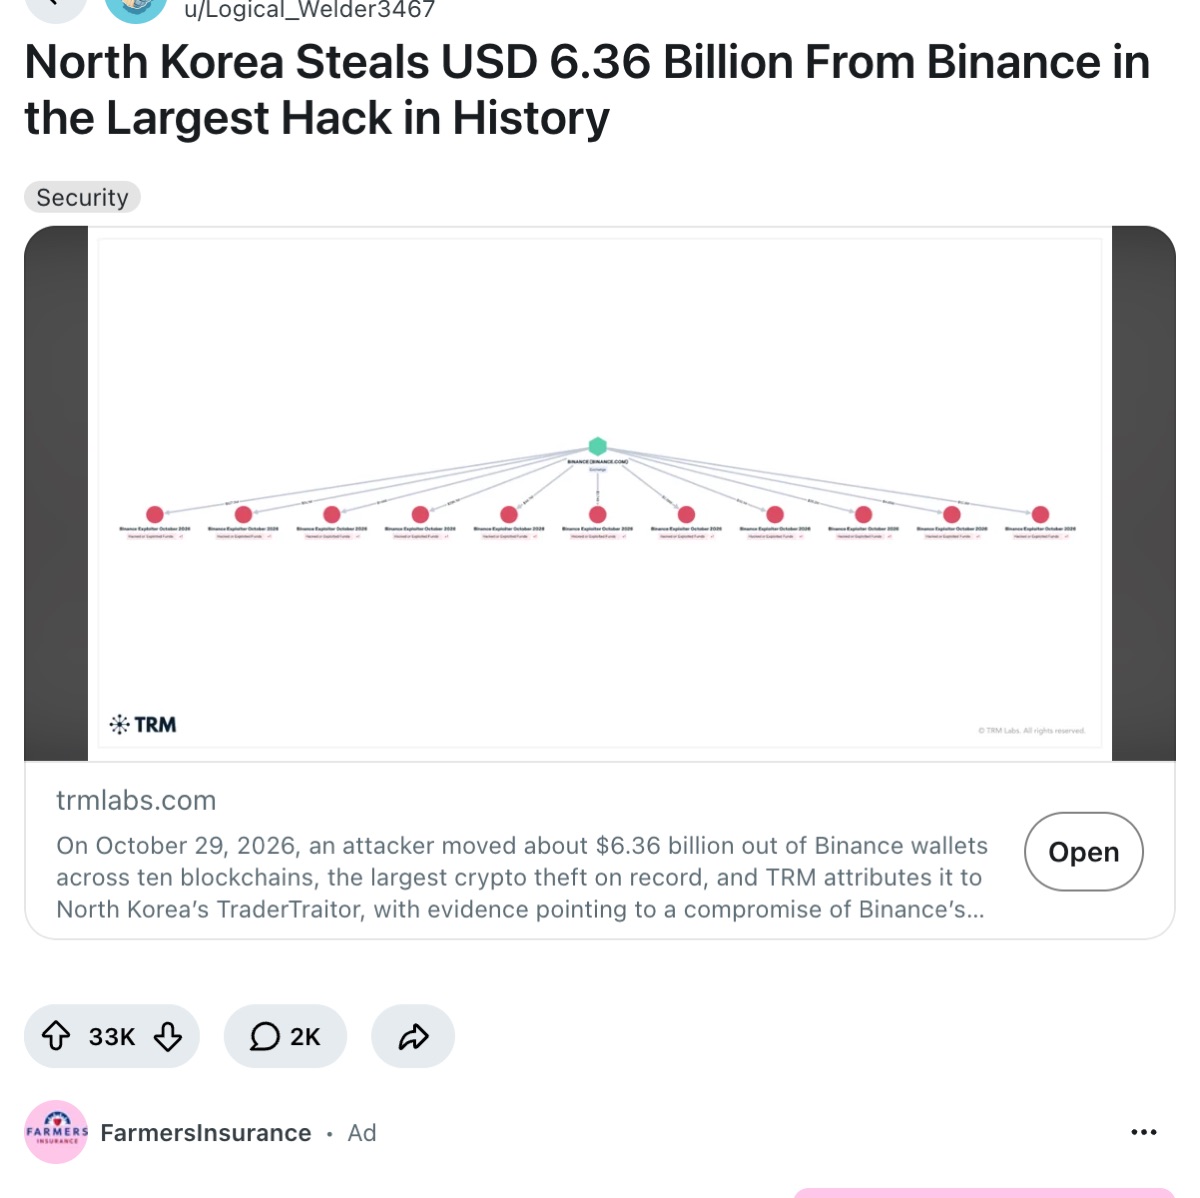
View original thread on Reddit
On X, the takes were immediate and viral.
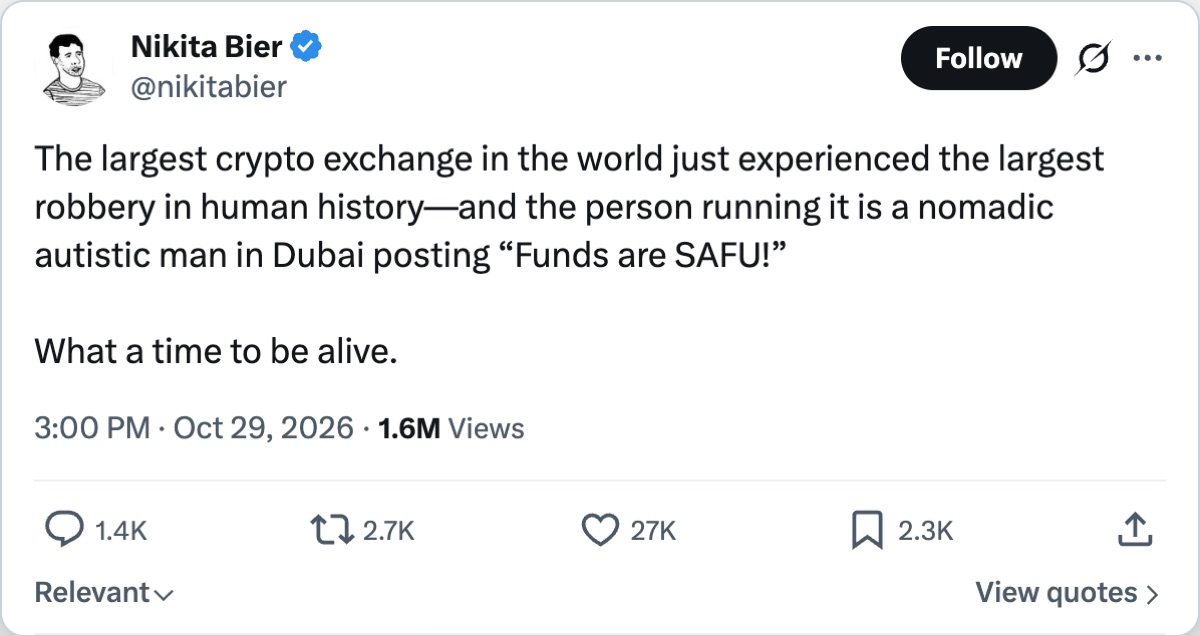
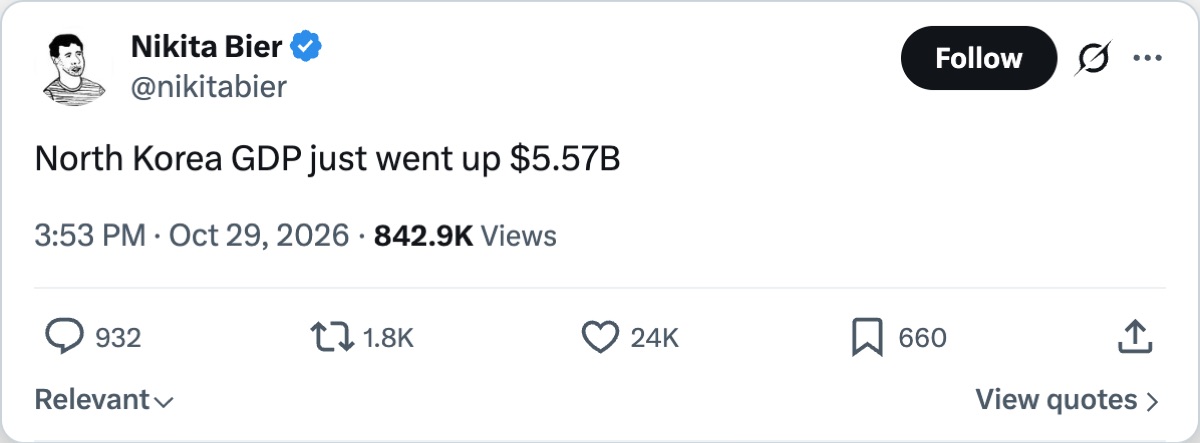
Nikita Bier's take pulled 27,790 likes and 1.6 million views. His follow-up was darker and funnier:
But Here Is Where It Gets Worse: Your IDE Was Backdoored
The Binance hack was the loudest event of the week. The Claude Code extension backdoor might be the most important.
On October 30, Phorion published an advisory revealing that the "official" Claude Code for VS Code extension on Cursor's marketplace had been compromised. Someone gained access to Cursor's marketplace and published a tampered version of the extension. The payload, injected into extension.js, executed before the extension's normal activation — no user interaction required.
Here is what the backdoor did:
- Planted an SSH key — appended an attacker-controlled Ed25519 key labeled
svc-telemetryto~/.ssh/authorized_keys - Opened a reverse tunnel — established an outbound SSH connection to 134.209.82.225, giving the operator direct access to the machine's SSH daemon
- Installed persistence — LaunchAgent on macOS (
com.apple.sysmond.plist),@rebootcron on Linux, scheduled task on Windows - Exfiltrated reconnaissance — sent hostname, username, OS, architecture, Git email, public IP, and the names of up to 40 environment variables matching
KEY|TOKEN|SECRET|PASS|AWS|GCP
Check now: Run grep svc-telemetry ~/.ssh/authorized_keys. If it returns a match, assume your machine is compromised. Kill the tunnel processes, remove the persistence artifacts, revoke the key, and rotate every credential accessible to that user account.
The Hacker News thread hit 706 points and 441 comments — the number-one story of the day. Anthropic engineer Felix clarified: "We're working with Cursor on this incident, but it wasn't a compromise of Anthropic's systems or employee laptops. A malicious actor used access to Cursor's marketplace to publish a tampered copy of the Claude Code extension, which we didn't build or publish."
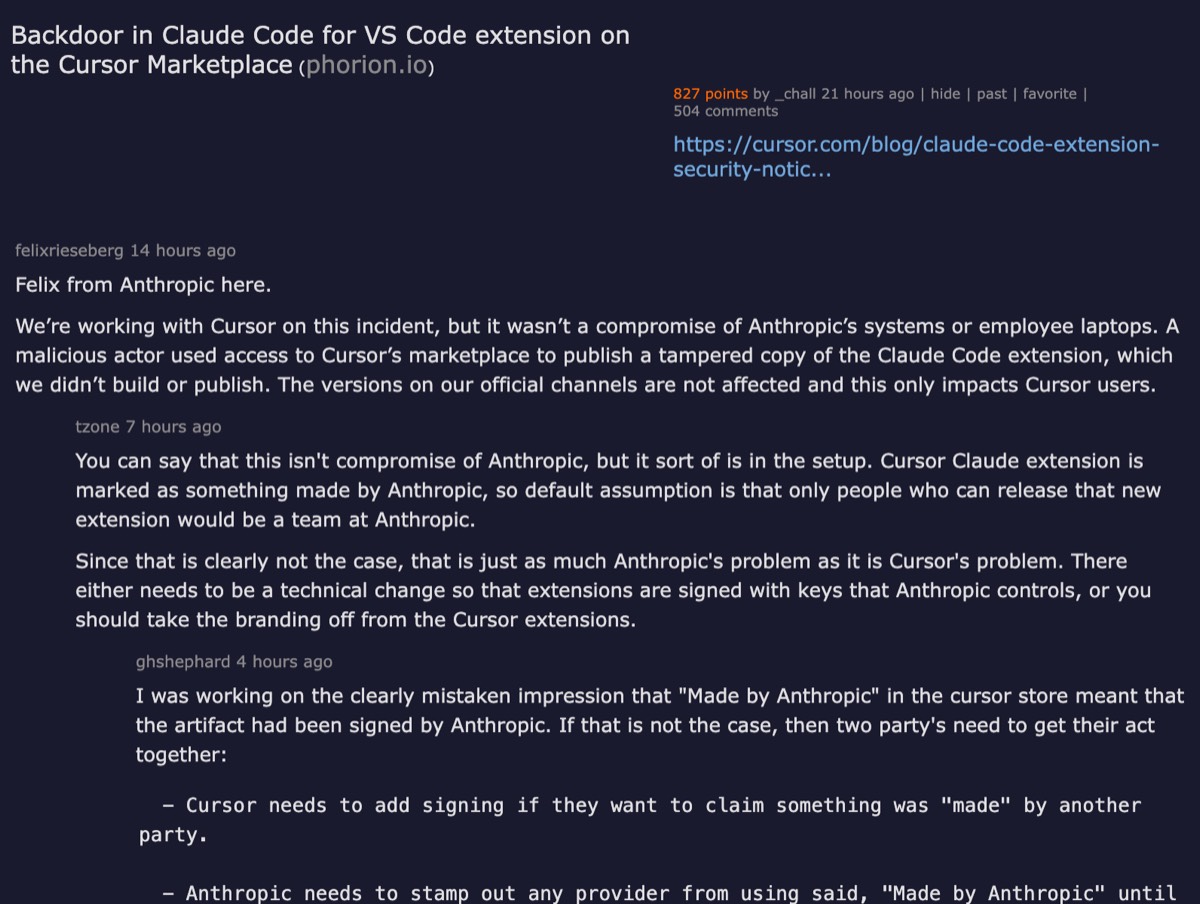
View original thread on Hacker News
This is the critical detail. The weak point was not the AI vendor. It was the marketplace — the same distribution channel that developers trust implicitly when they install "official" extensions. If your IDE extension marketplace can be compromised, every developer who installs from it is one update away from a backdoor.
We covered a similar pattern earlier this year when LiteLLM's supply chain was compromised via a poisoned Trivy dependency. The attack vector is evolving: from package managers to extension marketplaces. The target shifted from libraries you pip install to tools you trust inside your editor.
Azure: The Cloud Was Leaking Too
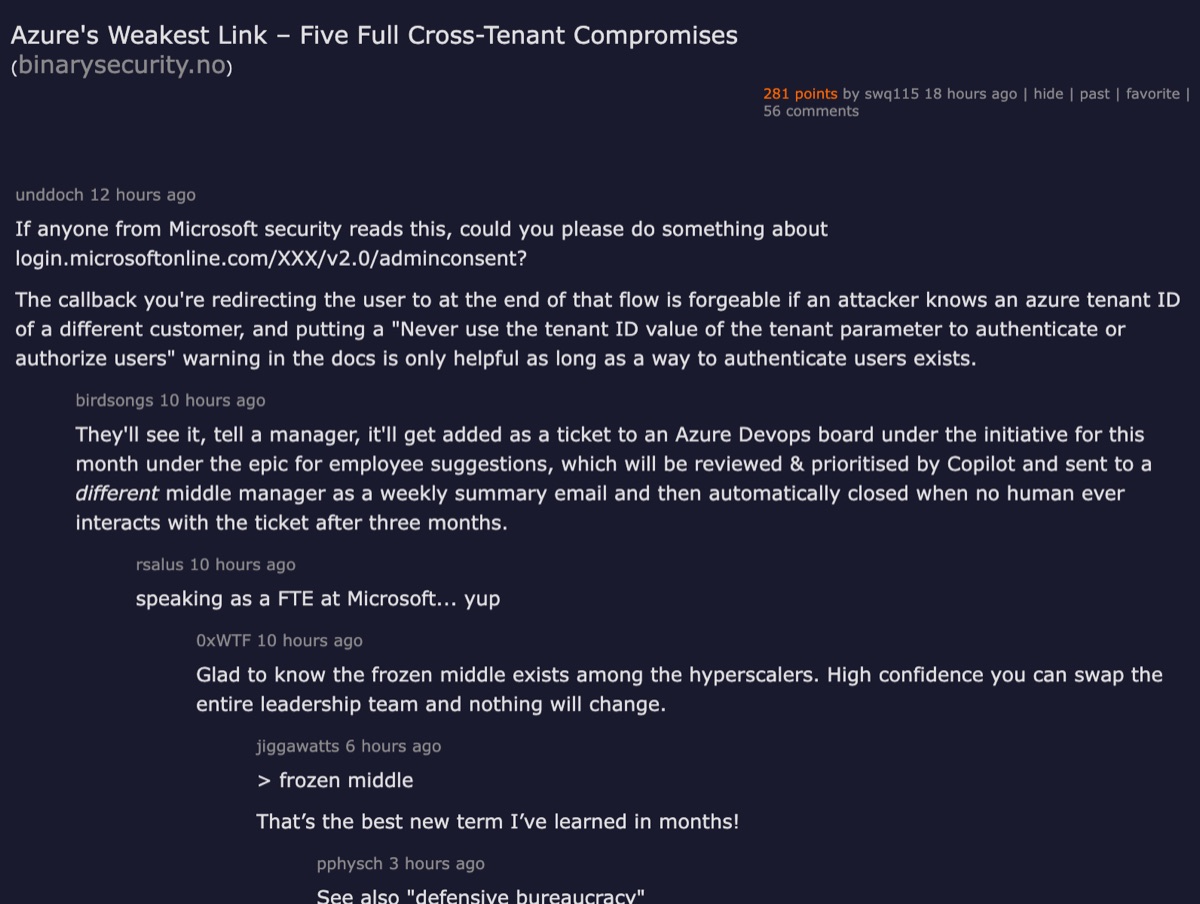
While the world focused on Binance and the Claude Code backdoor, Binary Security researcher Haakon Wik Gulbrandsrud quietly disclosed five cross-tenant elevation-of-privilege flaws in Azure API Connections — earning $200,000 in bug bounties.
The root cause is architectural. Azure Logic Apps call a shared Azure API Management (APIM) instance, which swaps the caller's connection credentials for the backend service's token. APIM has access to every connection — so security depends entirely on input validation layers. As the researcher put it: "The only thing stopping exploitation is really the layers of input validation."
Those layers failed five times:
- Path traversal in DynamicInvoke — read secrets from another tenant's Key Vault
- Undocumented sibling endpoints — allowed arbitrary SQL queries against a victim's Azure SQL database
- Consumption Logic Apps RuntimeUrl bypass — redirected calls to another connection's endpoint
- Validation bypass — traversal sequences slipped past pre-normalization checks
- Regression — a later fix stopped validating the original path, reopening the attack
View original thread on Hacker News
The HN thread carried a telling comment: "When it comes to the amount of cross-tenant leaks Azure looks to be way ahead the competition. Makes me wonder why enterprises still flock there."
The pattern: These are not sophisticated zero-days. They are validation errors — the same category of bug that has existed since the first web form. What changed is the blast radius: a single traversal sequence in a shared APIM instance can reach every tenant's secrets.
The Infrastructure Wave: Linode, Bunny CDN, AO3
The same day saw three more infrastructure providers disclose security incidents:
Linode posted a security incident notice with minimal details. The top HN comment (101 points) was prescient: "All companies should at this point invest a lot of money into defensive AI. In ~July the AI hit crypto and bitcoin, where it's the easiest to extract the most money. Now the AI powered attacks are hitting infra and SaaS. Next (~December), it will hit classic infrastructure, banks, small businesses."
Bunny CDN disclosed unauthorized access involving third-party server management software. A commenter clarified the real target: "Gcore themselves got hacked, not Bunny. Bunny was just an affected downstream, in only one of their POPs." This is supply-chain compromise at the infrastructure layer — the CDN provider's own provider was breached.
AO3 (Archive of Our Own) went dark for investigation, stating: "We detected evidence of a security incident on AO3. We are still in the early stages of response."
None of these individually would be front-page news. All of them in one day — that is a signal.
Nathan Lambert Reconsidered His Stance
The most intellectually honest response came from Nathan Lambert at Interconnects. Lambert has been one of the AI community's most prominent defenders of open-weight model releases, arguing that the cybersecurity risks of open models were overstated.
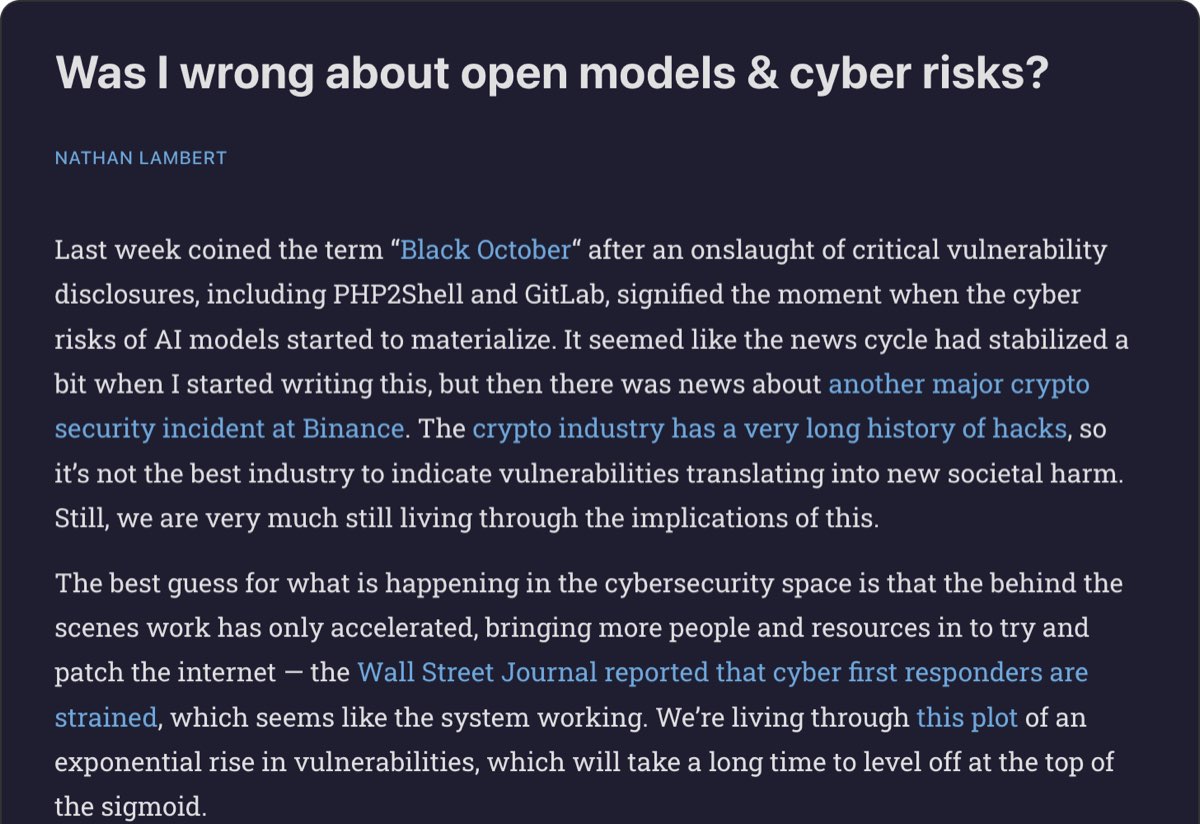
On October 30, he published "Was I wrong about open models & cyber risks?" — publicly stress-testing his own position against the Black October evidence.
His conclusion is nuanced. He still believes open models provide defensive balance and that closed models have contributed to more recent hacks. But he admits his previous framing was wrong: "'Fine' was the wrong word, since the coming shift is expensive and turbulent." He now gives more credit to safety researchers who warned about a new era of cyber instability.
View original article on Interconnects
The reader pushback in the comments is telling. One commenter notes that monthly CVE publications rose sharply from April to August 2026 — coinciding with the release of the first exploit-capable open model. Another argues that research disproportionately emphasizes offensive over defensive AI capabilities.
Contrarian Corner: The "Black October" narrative is pattern-matching on noise. Breaches happen all the time. Four infrastructure incidents in one day is within normal variance for a global internet. The Binance hack is crypto being crypto. The Claude Code backdoor is a marketplace trust issue, not an AI issue. None of these incidents are connected by anything other than the calendar. — But the HN community itself noticed the pattern. Five of twelve top stories being security incidents on a single day is far outside the norm for that forum. And the attack vectors are qualitatively different — they hit developer tools, cloud multi-tenancy, and CDN infrastructure simultaneously. The targets moved upstream.
The Pattern: Attacks Moved Upstream
Here is what connects these incidents beyond the calendar:
The Binance hack targeted signing infrastructure — not user accounts, not a smart contract bug, but the key management layer that everything else depends on.
The Claude Code backdoor targeted the developer toolchain — not the code developers write, but the tools they use to write it. An IDE extension is about as upstream as you can get in the software supply chain.
The Azure compromises targeted the shared control plane — not individual VMs or databases, but the API management layer that brokers access to all of them.
The CDN/hosting breaches targeted infrastructure providers' own providers — Gcore was hacked, Bunny was the downstream casualty. Linode's incident details remain sparse, but the pattern holds.
Every attack moved one level further upstream. That is the shift. Stealing cryptocurrency requires compromising a single target. Compromising a developer extension marketplace, a cloud control plane, or a CDN provider's infrastructure gives you access to thousands of downstream targets.
This is not random clustering. It is an optimization. If you are a nation-state attacker with AI-augmented capabilities, you attack the highest-leverage points in the system. And in October 2026, those points stopped being crypto exchanges and started being the infrastructure that runs everything else.
What This Means for You
If you are a developer, security engineer, or technical leader, here is your October action list:
1. Audit your IDE extensions today.
Run grep svc-telemetry ~/.ssh/authorized_keys on every machine. But more broadly: review what extensions you have installed and from where. The VS Code marketplace, Cursor marketplace, and their equivalents are now proven attack surfaces. Consider signing extensions, pinning versions, and reviewing extension permissions before install.
2. Check your SSH authorized_keys.
The Claude Code backdoor planted an SSH key. But any compromised tool could do the same. Set up a monitoring alert for changes to ~/.ssh/authorized_keys across your fleet.
3. Review Azure API Connection scoping. If you use Azure Logic Apps with API Connections, review the credentials each connection holds. Prefer narrowly scoped service principals over broad OAuth tokens. The Binary Security research shows that connection security depends on input validation layers that have failed five times.
4. Assume supply-chain attacks on developer tools are a first-class threat. This is the lesson of 2026: the attack surface is not just your dependencies (npm, pip, cargo) — it is your tools (IDE extensions, AI assistants, cloud management portals). We wrote about this when LiteLLM was compromised. The pattern is now confirmed.
5. Monitor your cloud provider status pages. The Linode, Bunny, and AO3 incidents were disclosed on status pages before they hit the news cycle. If you depend on infrastructure, subscribe to their incident feeds.
Jason Calacanis proposed on This Week in Startups that the tech industry should stop shipping new features for one month a year and focus exclusively on security patching — "No App November." It is half-joke, half-prophecy. We have already written about how AI vendor dependency is itself a risk. When your vendor's marketplace is the attack vector, the dependency becomes a liability.
The question is no longer "will my exchange get hacked." The question is: is your development environment already compromised?
The convergence of the Binance hack, the Claude Code backdoor, and the infrastructure breach wave is exactly the kind of AI-security intersection we track at ComputeLeap. For more on how AI models interact with cybersecurity, see our coverage of Claude Mythos and Project Glasswing.
ComputeLeap Team
The ComputeLeap editorial team covers AI tools, agents, and products — helping readers discover and use artificial intelligence to work smarter.
Join the discussion
Have thoughts on this article? Discuss it on your favorite platform:
Related articles
Brooks's Law Just Got Its First Exception in 50 Years
AI agents don't break Brooks's Law. They transform it. The HN #1 essay and 12 months of evidence reveal what actually changed.
Apple's iPhone Duo Is Cracking on Day One
The $1,999 iPhone Duo's inner display is cracking along the hinge within hours. Here's what iFixit found, what it costs to fix, and why waiting might be wise.
AI's Payoff Problem Is Bigger Than You Think
Apollo says zero returns outside Big Tech. 200K creative jobs gone. Middle management next. The AI reckoning is here.